Policy as Code for Regulated Teams: OPA & Kyverno
Sep 17, 2026
Guardrails belong in the platform, not the wiki.
Two live Kubernetes clusters — Gatekeeper on one, Kyverno on the other. The same manifest goes to both, and we watch what each one does with it. Chat calls the shots on which policy we break next.
What we cover:
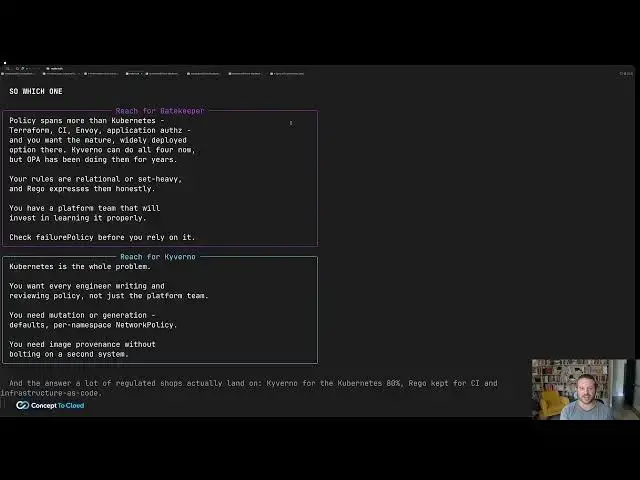
• OPA/Rego vs Kyverno — when to reach for each, honestly
• Real policies: no privileged pods, required labels, image provenance
• Enforcing at admission, and what audit mode actually records on each engine
• The question nobody asks until the audit: what happens to admission when the policy engine itself is down
• Mutation, resource generation and cosign image verification
• Where both engines are heading now that Kubernetes speaks CEL
Kyverno graduated CNCF in March 2026. Gatekeeper has spoken CEL since 3.18. Most OPA-vs-Kyverno comparisons are two years stale — this one isn't.
Concept to Cloud — book a discovery call.
Show More Show Less #Arts & Entertainment